Ethereum Miner - Mine and Earn free Ethereum Doloca.net: Online Booking - Hotels and Resorts, Vacation Rentals and Car Rentals, Flight Bookings, Activities and Festivals, Tour

Wednesday, June 3, 2020

Forerunner - Fast And Extensible Network Scanning Library Featuring Multithreading, Ping Probing, And Scan Fetchers


The Forerunner library is a fast, lightweight, and extensible networking library created to aid in the development of robust network centric applications such as: IP Scanners, Port Knockers, Clients, Servers, etc. In it's current state, the Forerunner library is able to both synchronously and asynchronously scan and port knock IP addresses in order to obtain information about the device located at that endpoint such as: whether the IP is online, the physical MAC address, and etc. The library is a completely object oriented and event based library meaning that scan data is contained within specially crafted "scan" objects which are designed to handle all data from results to exceptions.

Requirements
  • .NET Framework 4.6.1

Features
MethodDescriptionUsage
ScanScan a single IP for informationScan("192.168.1.1");
ScanRangeScan a range of IPs for informationScanRange("192.168.1.1", "192.168.1.255")
ScanListScan a list of IPs for informationScanList("192.168.1.1, 192.168.1.2, 192.168.1.3")
PortKnockPing every port of a single IPPortKnock("192.168.1.1");
PortKnockRangePing every port in a range of IPsPortKnockRange("192.168.1.1", "192.168.1.255");
PortKnockListPing every port using a list of IPsPortKnockList("192.198.1.1, 192.168.1.2, 192.168.1.3");
IsHostAlivePing a host N times for X millisecondsIsHostAlive("192.168.1.1", 5, 1000);
GetAveragePingResponseGet average ping response for a hostGetAveragePingResponse("192.168.1.1", 5, 1000);
IsPortOpenPing individual ports via TCP & UDPIsPortOpen("192.168.1.1", 45000, new TimeSpan(1000), false);

Examples

IP Scanning
Scanning a network is a commonplace task in this digital age and so I have taken the liberty to make this as simple as possible for any future programmer whom may wish to do such a thing in an easy way. The Forerunner library is completely object oriented, thus making it ideal for plug and play situations; the object for IP scanning is called an IPScanObject and it actually contains quite a few properties:
  • Address (String)
  • IP (IPAddress)
  • Ping (Long)
  • Hostname (String)
  • MAC (String)
  • isOnline (Bool)
  • Errors (Exception)
With the object in mind, let's try and create a new object and perform a scan using it. There are multiple ways to go about this, however, the simplest way to get started is to first create a new Scanner object so we can access our scanning methods. Next, create an IPScanObject and then set it to the Scan method with the IP you would like to enumerate; for example:

Synchronous
using System;
using Forerunner; // Remember to import our library.

namespace Example
{
class Program
{
static void Main(string[] args)
{
// Our IP we would like to scan.
string ip = "192.168.1.1";

// Create a new scanner object.
Scanner s = new Scanner();

// Create a new scan object and perform a scan.
IPScanObject result = s.Scan(ip);

// Output that we have finished the scan.
if (result.Errors != null)
Console.WriteLine("[x] An error occurred during the scan.");
else
Console.WriteLine("[+] " + ip + " has been successfully scanned!")

// Allow the user to exit at any time.
Console.Read();
}
}
}
Another way, which is my preferred method of operation, is to create a Scanner object and subscribe to the Event Handlers of things like ScanAsyncProgressChanged or ScanAsyncComplete, that way I have full control over my async methods; I can control how they're progress states affect my application and so on; for example:

Asynchronous
using System;
using System.Threading.Tasks;
using Forerunner; // Remember to import our library.

namespace Example
{
class Program
{
static void Main(string[] args)
{
// Our IP we would like to scan.
string ip = "192.168.1.1";

// Setup our scanner object.
Scanner s = new Scanner();
s.ScanAsyncProgressChanged += new ScanAsyncProgressChangedHandler(ScanAsyncProgressChanged);
s.ScanAsyncComplete += new ScanAsyncCompleteHandler(ScanAsyncComplete);

// Start a new scan task with our ip.
TaskFactory task = new TaskFactory();
task.StartNew(() => s.ScanAsync(ip));

// Allow the user to exit at any time.
Console.Read();
}

static void ScanAsyncProgressChanged(object sender, ScanAsyncProgressChangedEve ntArgs e)
{
// Do something here with e.Progress, or you could leave this event
// unsubscribed so you wouldn't have to do anything.
}

static void ScanAsyncComplete(object sender, ScanAsyncCompleteEventArgs e)
{
// Do something with the IPScanObject aka e.Result.
if (e.Result.Errors != null)
Console.WriteLine("[x] An error occurred during the scan.");
else
Console.WriteLine("[+] " + e.Result.IP + " has been successfully scanned!")
}
}
}

Port Knocking
I know what you're thinking. Port knocking? Yes, and no. The term doesn't mean port knocking in the traditional sense of connecting through a predefined set of ports, but rather just checking if any ports are actually open. It's literally "knocking" on a port in every sense of the word by trying to connect to each port and sending data. Just like with IP scanning, port knocking uses a custom object which is called a "Port Knock Scan Object" or PKScanObject for short. The PKScanObject actually contains a list of PKServiceObjects which in turn hold our port data; the service object contains the following properties:
  • IP (String)
  • Port (Int)
  • Protocol (PortType)
  • Status (Bool)
Port knocking is in similar fashion with IP scanning. First, create a Scanner object. Next, create a new PKScanObject and set it to the PortKnock method with the IP of your choosing, then display your results; for example:

Synchronous
using System;
using Forerunner; // Remember to import our library.

namespace Example
{
class Program
{
static void Main(string[] args)
{
// Our IP we would like to scan.
string ip = "192.168.1.1";

// Create a new scanner object.
Scanner s = new Scanner();

// Create a new scan object and perform a scan.
PKScanObject result = s.PortKnock(ip);

// Output that we have finished the scan.
if (result.Errors != null)
Console.WriteLine("[x] An error occurred during the scan.");
else
Console.WriteLine("[+] " + ip + " has been successfully scanned!")

// Display our results.
foreach (PKServiceObject port in result.Services)
{
Console.WriteLine("[+] IP: " + port .IP + " | " +
"Port: " + port.Port.ToString() + " | " +
"Protocol: " + port.Protocol.ToString() + " | " +
"Status: " + port.Status.ToString());
}

// Allow the user to exit at any time.
Console.Read();
}
}
}
Lastly, I will show you a simple example of port knocking asynchronously. It is essentially the same as port knocking synchronously except for the fact that you can use events to your advantage. You can get progress updates without having to worry about UIs crashing or systems being in a locked state; for example:

Asynchronous
using System;
using System.Threading.Tasks;
using Forerunner; // Remember to import our library.

namespace Example
{
class Program
{
static void Main(string[] args)
{
// Our IP we would like to scan.
string ip = "192.168.1.1";

// Setup our scanner object.
Scanner s = new Scanner();
s.PortKnockAsyncProgressChanged += new PortKnockAsyncProgressChangedHandler(PortKnockAsyncProgressChanged);
s.PortKnockAsyncComplete += new PortKnockAsyncCompleteHandler(PortKnockAsyncComplete);

// Start a new scan task with our ip.
TaskFactory task = new TaskFactory();
task.StartNew(() => s.PortKnockAsync(ip));

// Allow the user to exit at any time.
Console.Read();
}

static void PortKnockAsyncProgressChanged(ob ject sender, PortKnockAsyncProgressChangedEventArgs e)
{
// Display our progress so we know the ETA.
if (e.Progress == 99)
{
Console.Write(e.Progress.ToString() + "%...");
Console.WriteLine("100%!");
}
else
Console.Write(e.Progress.ToString() + "%...");
}

static void PortKnockAsyncComplete(object sender, PortKnockAsyncCompleteEventArgs e)
{
// Tell the user that the port knock was complete.
Console.WriteLine("[+] Port Knock Complete!");

// Check if we resolved an error.
if (e.Result == null)
Console.WriteLine("[X] The port knock did not return any data!");
else
{
// Check if we have any ports recorded.
if (e.Result.Services.Count == 0)
Console.WriteLine("[!] No ports were open during the knock.");
else
{
// Display our ports and their details.
foreach (PKServiceObject port in e.Result.Services)
{
Console.WriteLine("[+] IP: " + port.IP + " | " +
"Port: " + port.Port.ToString() + " | " +
"Protocol: " + port.Protocol.ToString() + " | " +
"Status: " + port.Status.ToString());
}
}
}
}
}
}

Credits
Icon: monkik
https://www.flaticon.com/authors/monkik


via KitPloit

Related articles


What Is Cybersecurity And Thier types?Which Skills Required To Become A Top Cybersecurity Expert ?

What is cyber security in hacking?

The term cyber security  refers to the technologies  and processes designed  to  defend computer system, software, networks & user data from unauthorized access, also from threats distributed through the internet by cybercriminals,terrorist groups of hacker.

Main types of cybersecurity are
Critical infrastructure security
Application security
Network Security 
Cloud Security 
Internet of things security.
These are the main types of cybersecurity used by cybersecurity expert to any organisation for safe and protect thier data from hack by a hacker.

Top Skills Required to become Cybersecurity Expert-

Problem Solving Skills
Communication Skill
Technical Strength & Aptitude
Desire to learn
Attention to Detail 
Knowledge of security across various platforms
Knowledge of Hacking
Fundamental Computer Forensic Skill.
These skills are essential for become a cybersecurity expert. 
Cyber cell and IT cell these are the department  in our india which provide cybersecurity and looks into the matters related to cyber crimes to stop the crime because in this digitilization world cyber crime increasing day by day so our government of india also takes the immediate action to prevent the cybercrimes with the help of these departments and also arrest the victim and file a complain against him/her with the help of cyberlaw in our constitution.


More info
  1. Pentest Stages
  2. Pentest Standard
  3. Hackintosh
  4. Pentest Security
  5. Hacking Vpn
  6. Pentest Practice
  7. Pentest Online Course
  8. Hacking Vpn
  9. Pentesting Tools
  10. Hacking Wifi
  11. Pentest Open Source
  12. Pentest Basics
  13. Hacking Google

MyPublicInbox: Hackers, Músicos, Periodistas Y Artistas @Mypublicinbox1 @0xWord

Cada cierto tiempo os traigo una pequeña actualización de cómo está yendo el proyecto de MyPublicInbox, con algunas novedades en cuanto a nuevas características, y algunos de los nuevos perfiles públicos que se han dado de alta en la plataforma. Actualmente el número de usuarios de la plataforma es más de 2.500 y cada día crece más y más deprisa, lo que nos anima mucho.

Figura 1: MyPublicInbox: Hackers, Músicos, Periodistas y Artistas

Hoy os he querido traer algunos perfiles públicos, y el fin de semana os publicaré algunos de los nuevos servicios que hemos habilitado para los perfiles públicos de la plataforma, por si os son de utilidad para mejorar vuestra presencia en Internet de una forma más segura.

Aurora Beltrán (Tahures Zurdos)

Si has seguido la música Rock en Español, es imposible que no hayas escuchado algunas de las canciones de Tahures Zurdos, con esa voz tan personal y bonita, como tiene Aurora Beltrán. Azul, Tatuados, Llueve, o Tocaré, son algunos de los temazos que forman parte del repertorio que siguen dando en todos conciertos en que los vayas a ver. Ahora puedes contactar con Aurora Beltrán en MyPublicInbox.

Figura: Contactar con Aurora Beltrán en MyPublicInbox

Y si no la has visto tocando y cantando nunca, merece la pena que veas alguna de sus actuaciones. Os dejo este "Que entre la luz" que está en Youtube para que disfrutes un poco de su música.


Figura: Tahures Zurdos "Que entre la luz"


Desde los 17 años trabajando como periodista, Irma Soriano es un referente en la comunicación en este país. Ha hecho televisión, radio y ahora redes sociales. Es una de las grandes de este país y ha trabajado con maestros como Iñaki Gabilondo o Jesús Hermida. Ahora la tienes disponible a través de su buzón en MyPublicInbox.

Figura: Contactar con Irma Soriano

Sinvergonza

Uno de los cómicos que hay que ir a ver en La Chocita de El Loro de Madrid en cuanto que pasemos de fase. Gonzalo Jiménez, conocido con el nombre de Sivergonza, tiene uno de esos espectáculos para destornillarse de risa. Ahora, si buscas un humorista para amenizar cualquier acto, le tienes disponible en su buzón de contacto público en MyPublicInbox.

Figura: Contactar con Gonzalo Jiménez "Sinvergonza"


Hablar de Nico sin dejarme llevar es difícil. Nico Waisman es de los mejores profesionales y personas que he conocido en el mundo de la seguridad informática. Ha sido el alma de Immunity, ponente en BlackHat en muchas ocasiones, uno de los que más ha apoyado la creación de la Ekoparty, y ahora es un Senior VP en GitHub donde dirige el laboratorio de investigación en seguridad. Y entre sus méritos cuenta con haber dado una charla con Chema Alonso y haberse tomado muchas cervezas con él. Ahora está en MyPublicInbox donde puedes contactar con uno de los mejores hackers de nuestra generación. El gran Nico Waisman.

Figura: Contactar con Nico Waisman

Periodista, y actualmente subdirectora del programa de radio "La mañana de Federico" en la emisora de radio de "Es Radio" donde trabaja con Federico Jiménez Losantos, Isabel González es ahora también un perfil público de MyPublicInbox. Ahora puedes contactar directamente con ella a través de su buzón público.

Figura: Contactar con Isabel González

Pocos pueden decir que han lanzado una empresa, pero en el caso de Gallir, poner en tu CV que fundaste Menéame es algo diferente y especial. Profesor en la Universidad de las Islas Baleares, experto en Inteligencia Artificial, Big Data, y trabajador incansable. Ricardo Galli es un ejemplo de esos "Wozniaks" creadores en el mundo de las empresas tecnológicas. Ahora puedes contactar con él en MyPublicInbox.

Figura: Contactar con Ricado Galli

Esta hacker de las tablas se ha metido a la difícil y divertida tarea de aprender a hacer surf o skate después de los 40 años de edad, que es cuando yo aprendí a montarme sobre mi tabla. Me encantan sus vídeos y su motivación, y si te gusta el deporte y quieres disfrutar del placer de la tabla sobre asfalto o sobre olas, puedes contactar con ElenaSurfea a través de su buzón en MyPublicInbox.

Figura: Contactar con Elena Gómez aka Elena Surfea

Autora de varios libros sobre delitos informáticos, privacidad, Laura Davara es abogada especialista en protección de datos y derecho en redes sociales, además de formadora en materia de privacidad, GDPR y el trabajo de los DPO. Es socia del despacho de abogados Davara&Davara y puedes contactar con ella para cualquier consulta profesional a través del buzón público de Laura Davara en MyPublicInbox.

Figura: Contactar con Laura Davara


Es periodista y experta en relaciones con medios de comunicación.  Ayuda a aumentar la visibilidad de profesionales independientes, Pymes y Startups en los medios, convirtiéndolos en fuente de información para los periodistas. Carolina lleva años dedicándose a la comunicación corporativa y dirige "Influenzzia", su gabinete de prensa para empresas, con bastante éxito. Si quieres aumentar la visibilidad de tu negocio haciéndole formar parte de las noticias y creando enlaces de calidad; elevar tu prestigio como profesional y generar confianza en inversores y clientes potenciales. Puedes contactar con ella en su buzón en MyPublicInbox.

Figura: Contactar con Carolina Bonilla

Nico Castellano

Y para completar esta lista, dejo a Nico Castellano, uno de los impulsores del hacking y el movimiento de las CONs en España. Es el "alma" detrás NoCONname, el congreso para hackers más longevo que se realiza en nuestro país. Por este congreso hemos pasado casi todos los ponentes del mundo del hacking y la seguridad informática, y cuenta con haber tenido a ilustres de la historia hablando allí. Ahora puedes contactar con Nico Castellano en su buzón en MyPublicInbox.

Figura: Contactar con Nico Castellano

Y estos son los que os he seleccionado hoy. Como podéis ver, el proyecto sigue vivo y creciendo a muy buen ritmo. Si quieres ver más perfiles, puedes verlo en la lista de Perfiles Públicos, y si quieres tener tu propio buzón en MyPublicInbox sabes que puedes hacerlo vía tu cuenta de Twitter, o puedes solicitarlo escribiendo a Ari donde revisarán tu petición.

Saludos Malignos!

Más Referencias:


Autor: Chema Alonso (Contactar con Chema Alonso)

More articles


How To Hack Any Game On Your Android Smartphone

How To Hack Any Game On Android 2018

How To Hack Any Game On Your Android Smartphone

By hacking android game you can unlock all the levels, use any resource according to your wish and lots more. Proceed with the method shown below to hack any game on your Android. But sometimes while playing our favorite game we get short on our resources that are needed to play that game, like power, weapons or lives etc. That consequence really becomes bothersome, so to overcome this we are here with the trick How To Hack Any Game On Android.

Today millions of character are using the android phone. Now an Android device enhances significant part of our life. Everyone loves to play games on their android device. There are lots of cool games that are today available on your Android device in Google Play Store.


How To Hack Any Game On Android 2018

Hack Any Game On Android
How To Hack Any Game On Your Android Smartphone
Now it's time to hack into the game and use any resources that you want to play at any level of the game. The method is really working and will let you alter the game according to your wish. Just proceed with simple steps below.

Steps To Hack Any Game On Android

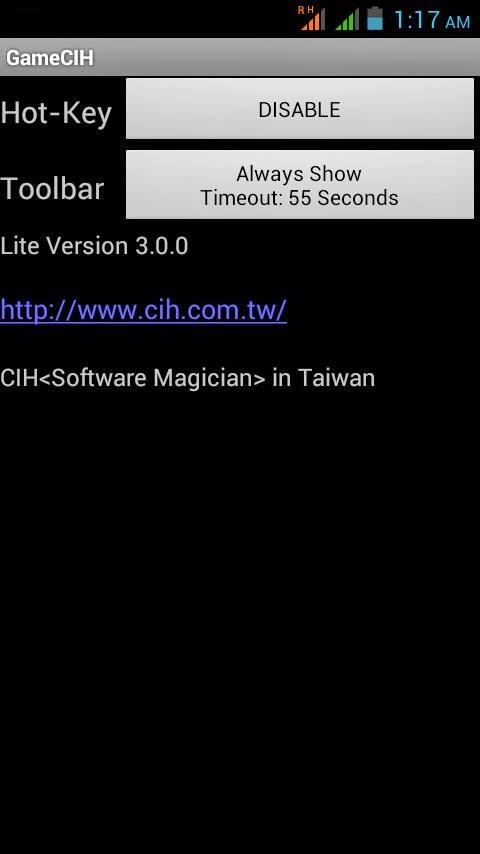
Step 1. First of all after rooting your android device open the GameCIH App. It will ask you for superuser access, grant it.(This will only come if you have properly rooted your android device. Now on the home screen of this app, you will see Hot-Key option, select any of them which you feel more convenient while using in your android.
Hack Any Game On Android
How To Hack Any Game On Your Android Smartphone
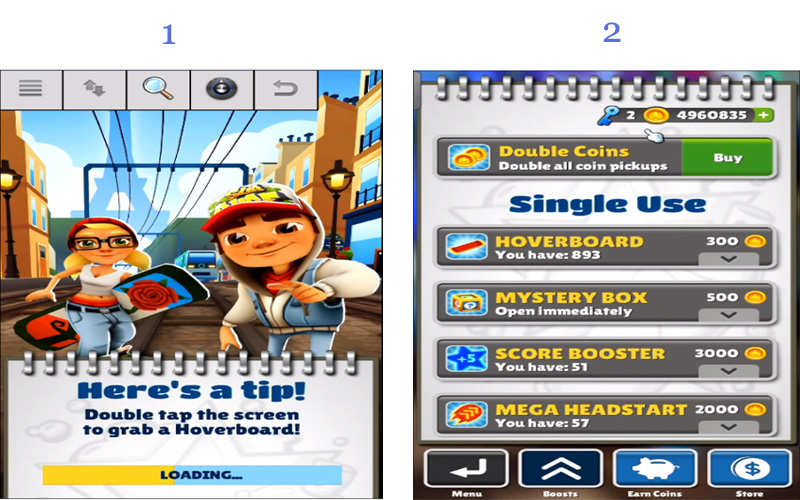
Step 2. Now open the game that you want to hack into your android device. Now pause the game and access the hotkeys displaying there, select any value that you want to edit in your game. Like any of text value like keys of subway surfer game.
Hack Any Game On Android.2
How To Hack Any Game On Your Android Smartphone
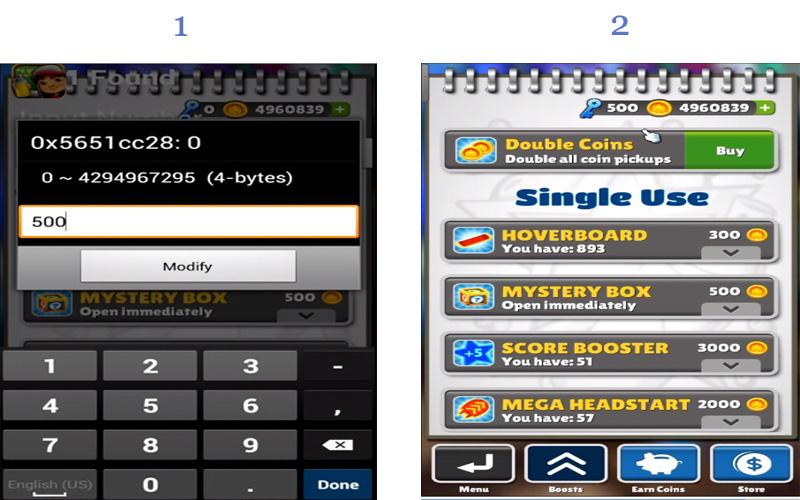
Step 3. Enter your desired value in the text field box appeared there and click on done. Now you will see default value will get replaced with your value. Similarly, you can alter any values in any of the game according to your wish.
Hack Any Game On Android.3
How To Hack Any Game On Your Android Smartphone
That's it game hacking is done, Now you can access any resources using this hack.
So above is all about Hack Any Game On Android. With the help of this trick, you can alter any coins, lives, money, weapons power and lots more in any of your favorite android game and can enjoy the unlimited game resources according to your wish.

Using Game Guardian

Game Guardian Apk is one of the best apps which you can have on your Android smartphone. With the help of this app, you can easily get unlimited coins, gems and can perform all other hacks. However, Game Guardian Apk needs a rooted Android smartphone to work. Here's a simple guide that will help you.
Step 1. First of all, you need to download the latest version of Game Guardian on your Android smartphone from the given download link above or below.
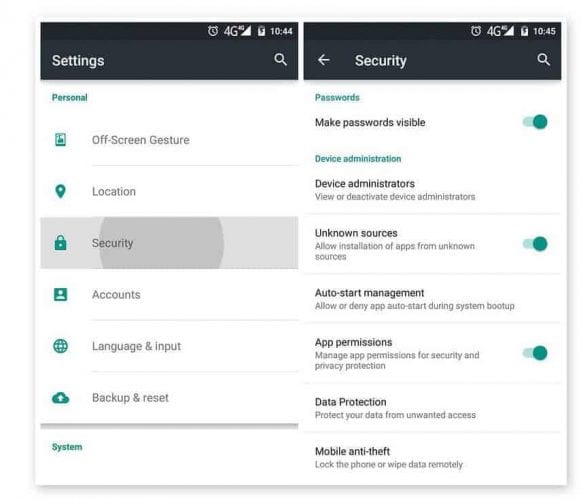
Step 2. After downloading on your smartphone, you need to enable the Unknown Source on your device. For that, you need to visit Settings > Security > Unknown Sources
Using Game Guardian
Using Game Guardian
Step 3. Now install the app and then press the home button to minimize the app. Now open any game that you want to hack. You will see an overlay of Game Guardian App icon. Tap on it.
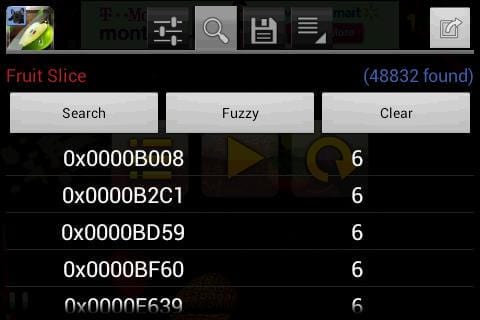
Step 4. Now you need to tap on the Search Button and set the value. If you don't know the values, then simply set it to auto.
Using Game Guardian
Using Game Guardian
Step 5. You need to search for the value which you want to hack like money, gem, health, score etc. You can change all those values. Suppose, if you need to decrease the number of values, you need to scan again for the new value.
Using Game Guardian
Using Game Guardian
Step 6. Finally, you need to select all the values and then change it to infinite numbers like '9999999' or whatever you want.
Using Game Guardian
Using Game Guardian
That's it, you are done! This is how you can use Game Guardian Apk to hack games on your Android smartphone.
With this, you can play a game at any levels without any shortage of any resource that can interrupt your gameplay. Hope you like this coolest android game hack. Don't forget to share it with others too.

Related word


Tuesday, June 2, 2020

Hacking PayPal's Express Checkout


Do you know what is happening in the background when you buy something in an online shop using PayPal?

In this post we will tackle the following problems:
  • How can PayPal's API be tested?
  • How does PayPal's Express Checkout work? You can find the detailed report here.
  • How can we debit more money than authorized?

How PayPal's API can be tested?

PayPal's Sandbox API

PayPal offers a feature called PayPal Sandbox Accounts, which mimics the production API. The basic idea is that a normal user/shop can test the API and make transactions without actually transferring money. This is the perfect tool for developers to test their API integration.

Access to all messages

The next question is how to get access to all messages. All browser-related messages can be inspected, intercepted, and modified via BurpSuite. The main problem here is how to get access to the server-to-server exchanged messages: the messages exchanged between PayPal and a shop. In order to solve this problem, we deployed our own shop. For this purpose we used Magento, which already has a PayPal integration.
Once we have our own controlled shop, we can enforce Magento to send all request through a proxy.
In the following picture you can see our setup.

Test suite for analyzing PayPal's API [1]

In order to capture the traffic between our Magento hhop and PayPal we proceeded as follows:
  • We configured Magento to use a proxy running on localhost:8081.
  • We connected the proxy port on the virtual machine with our local machine via SSH remote port forwarding by issuing the following command
    ssh -N -R 8081: localhost :8081 <IP of Magento shop>
  • We configured BurpSuite running on our local machine to listen on Port 8081 for incoming requests.
Now, we were able to see the entire traffic.
Please note that we uses our own, custom Magento shop in order to be able to test Paypal's API.

PayPal's Express Checkout

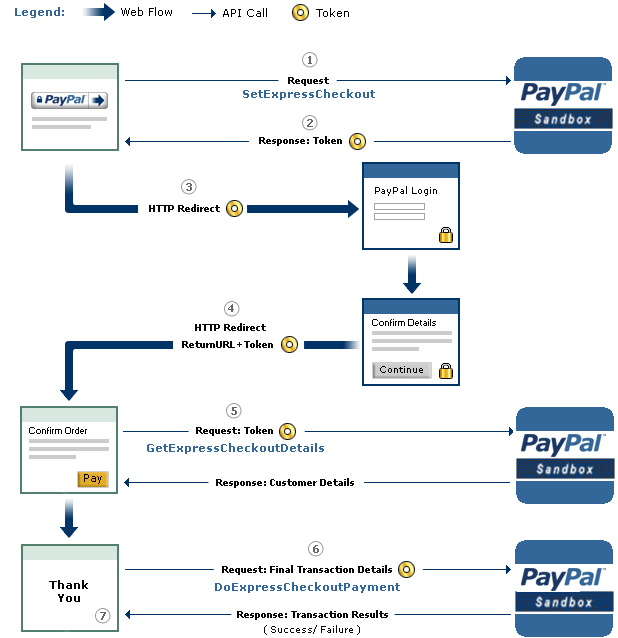
An overview of the checkout procedure is depicted in the following:

PayPal's Express Checkout [2]


Step 1: Magento tells the PayPal API where to redirect the user after authorizing the transaction via the parameter RETURNURL and requests a token for this transaction.
Step 2: The PayPal API provides Magento with the token.
Step 3: Magento redirects the user to PayPal's website. The redirect contains the token from the previous step.
Step 4:  The user authorizes the transaction. As a result, he will be redirected back to Magento (RETURNURL) with the token.
Step 5: Magento issues a request to the PayPal API to get the transaction details.

Step 6: Magento signals the PayPal API to execute the transaction.

Step 7: Magento serves the success page.

A more detailed view of the protocol and all parameters is shown on page 16 in the full version. We will concentrate only on step 6 and the parameters relevant for the attack.

The Attack

The goal of the attack is to let a shop (in our case Magento) debit more money than authorized by the PayPal user. The core of the attack is Step 6 -- DoExpressCheckoutPayment. Let's get a deeper look at this message:

Magento can raise the authorized amount and debit more money from the user's account

  • The shop sends the token, which was issued in the first step of the protocol and identifies uniquely the transaction through all steps. 
  • The PayerID referring to the user that authorized the payment.
  • The AMT defining the amount, which will be transferred.
  • The API Credentials authenticating Magento on PayPal.
  • The Version pointing to the release number of the API.

As one can imagine, the core problem we found was the change of the AMT parameter. This value can be freely chosen by the shop, despite the fact that the user has authorized a different amount.

We tested only the SandBox API, but refused to test the production API in order to avoid problems. We promptly contacted PayPal's security team and described the problem hoping that PayPal can and will test the production API against the attack.

The response of PayPal can be summarized as follows:
  • We don't get any BugBounty since we only tested the Sanbox API. (Fair enough)
  • In the Production API PayPal this flexibility is a wanted feature. Thus, PayPal allows a merchant to charge for shipping and/or other expenses different amounts. Any malicious behavior can be detected by PayPal. In case of fraudulent charges the consumer are protected by the Buyer Protection policy.
... but the Sandbox API was nevertheless fixed.

Authors of this Post

Daniel Hirschberger
Vladislav Mladenov
Christian Mainka (@CheariX)


[1] BurpSuite Logo
[2] PayPal Express CheckoutRead more

Joomla Resources Directory (JRD) Portal Suffers Data Breach

Joomla, one of the most popular Open-source content management systems (CMS), last week announced a new data breach impacting 2,700 users who have an account with its resources directory (JRD) website, i.e., resources.joomla.org. The breach exposed affected users' personal information, such as full names, business addresses, email addresses, phone numbers, and encrypted passwords. The

via The Hacker News

Related links


  1. Hacking Tutorials
  2. Hacker Lab
  3. Hacking Youtube
  4. Basic Pentest 1 Walkthrough
  5. Pentest Companies
  6. Pentestmonkey Sql Injection
  7. Pentest Dns
  8. Pentest Example Report
  9. Pentest Uk
  10. Pentest Report
  11. Hacker Wifi Password
  12. Hacker Attack
  13. Pentest Wifi
  14. Hacking The System
Ethereum Miner - Mine and Earn free Ethereum